When discussing cybersecurity, EDR and MDR are two terms that often come up. While related, they represent distinct approaches to threat detection and response. Here's a breakdown:
EDR (Endpoint Detection and Response):
Focus:
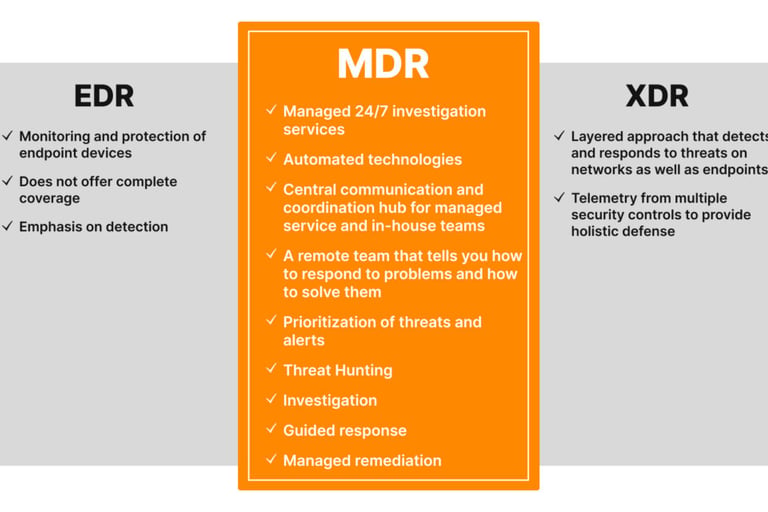
EDR primarily focuses on monitoring and securing individual endpoints (laptops, desktops, servers, etc.).
It collects and analyzes endpoint data to detect suspicious activities and potential threats.
Capabilities:
Real-time monitoring of endpoint activity.
Detection of malicious behavior.
Investigation and analysis of security incidents.
Tools for threat response and remediation.
Key takeaway:
EDR provides the tools and visibility needed to identify and respond to threats on individual devices.
MDR (Managed Detection and Response):
Focus:
MDR is a service that combines EDR technology with human expertise.
It involves a third-party provider that monitors an organization's security environment and responds to threats.
Capabilities:
24/7 threat monitoring and analysis.
Proactive threat hunting.
Incident response and remediation.
Access to security experts.
Key takeaway:
MDR provides a managed security service that offloads the burden of threat detection and response to a team of experts.
In essence:
EDR is a technology.
MDR is a service that often utilizes EDR technology.
Here's a simple analogy:
EDR is like having a sophisticated home security system with sensors and alarms.
MDR is like hiring a security company to monitor that system and respond to any alarms.
Therefore, MDR builds upon the capabilities of EDR by adding the crucial element of human expertise and proactive management.